

TL; DR
- CERT-In rated a batch of Chrome flaws critical in advisory CIVN-2026-0544.
- Desktop builds older than 157.0.8103.50 are affected; one flaw is reportedly exploited.
- Update Chrome through Help, About Google Chrome, then relaunch; Google’s newest build is 157.0.8103.78.
Most of us take our web browser for granted: it’s always there, it always works. We only think about it when something goes wrong. A notice from the Government of India is an excuse to take it seriously, especially if you browse on a laptop or desktop in India.
Also Read: Jensen Huang Resigns as Nvidia CEO: The Company Names Colette Kress As The Interim CEO
What Has CERT-In Flagged In Google Chrome?
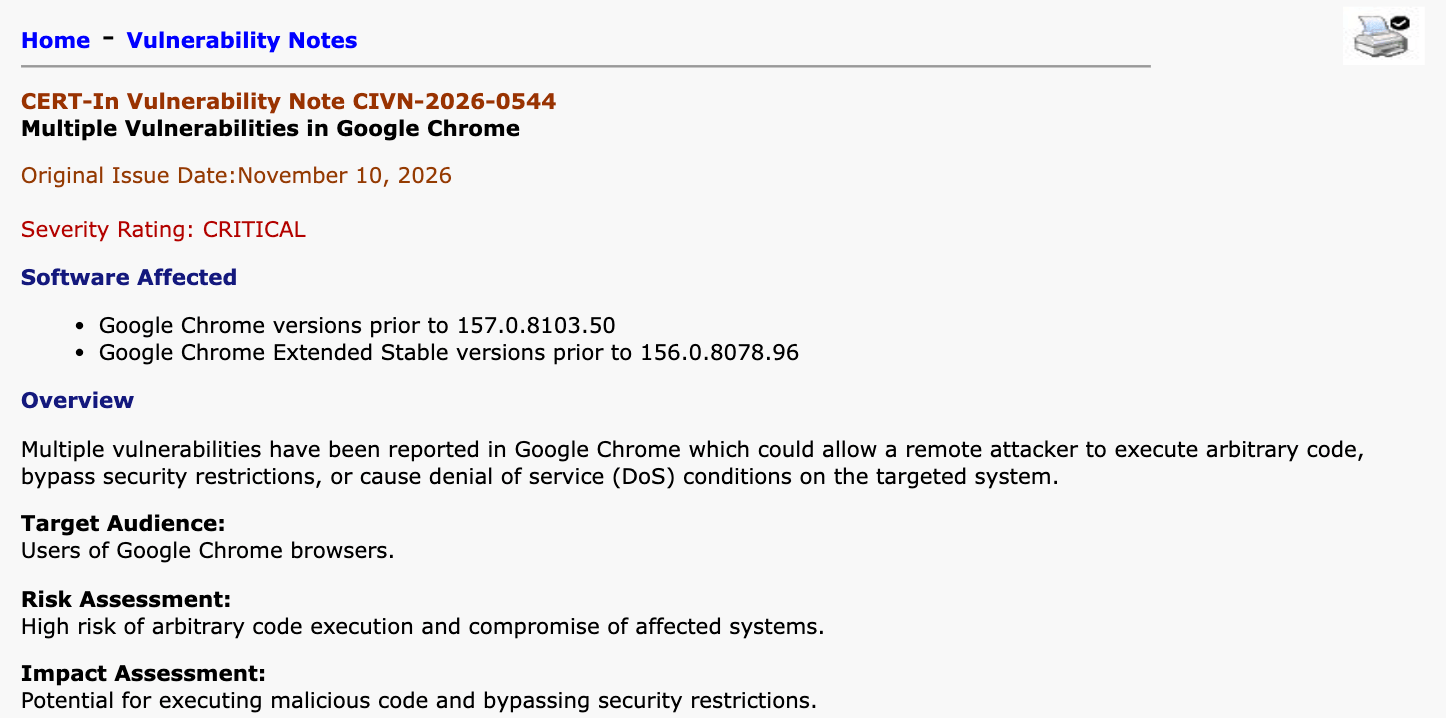
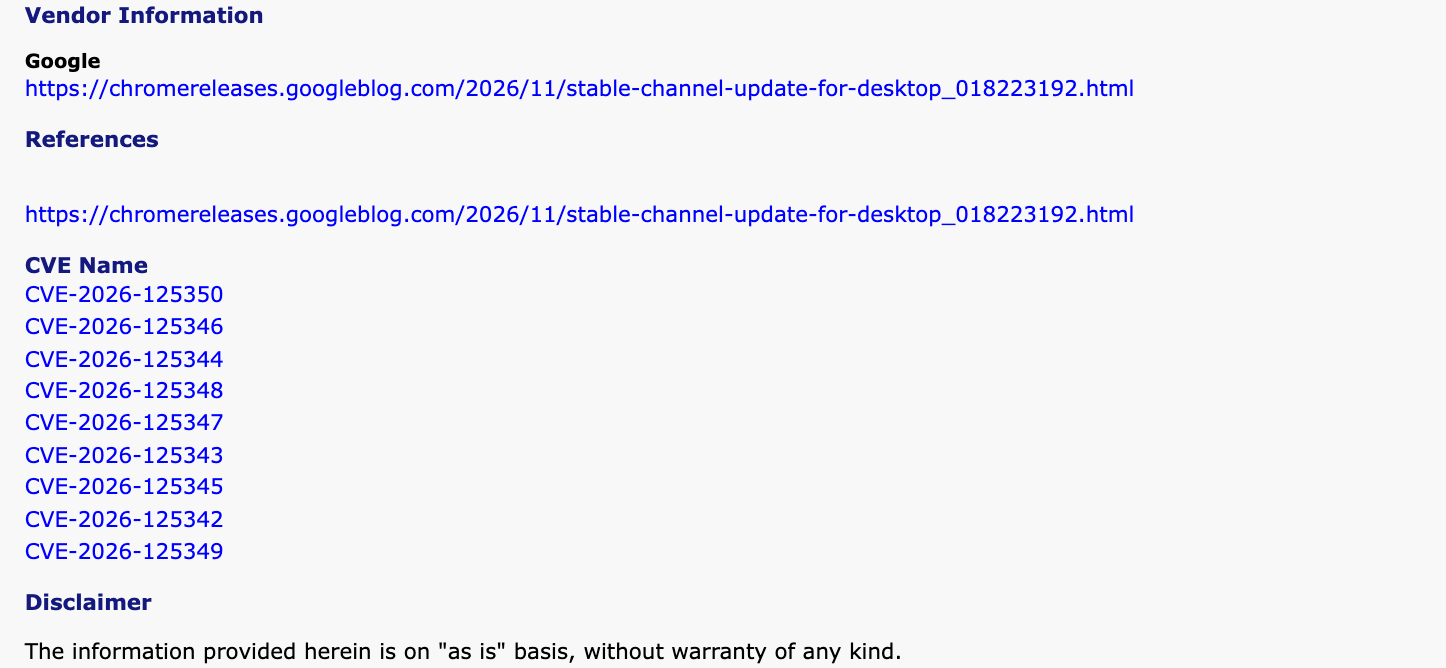
India’s cybersecurity agency, CERT-In, issued advisory CIVN-2026-0544 on November 10, 2026. The advisory rated several Google Chrome flaws as critical. The advisory notes a “high risk of arbitrary code execution and compromise of affected systems.”
The impact assessment, as mentioned in the advisory, states that there’s “potential for executing malicious code and bypassing security restrictions.” Those vulnerabilities already exist in Google Chrome and can be exploited for multiple reasons.
Also Read: vivo X500 Series India Launch Date Confirmed: November 26 with Watch GT 2 and a 400mm Extender
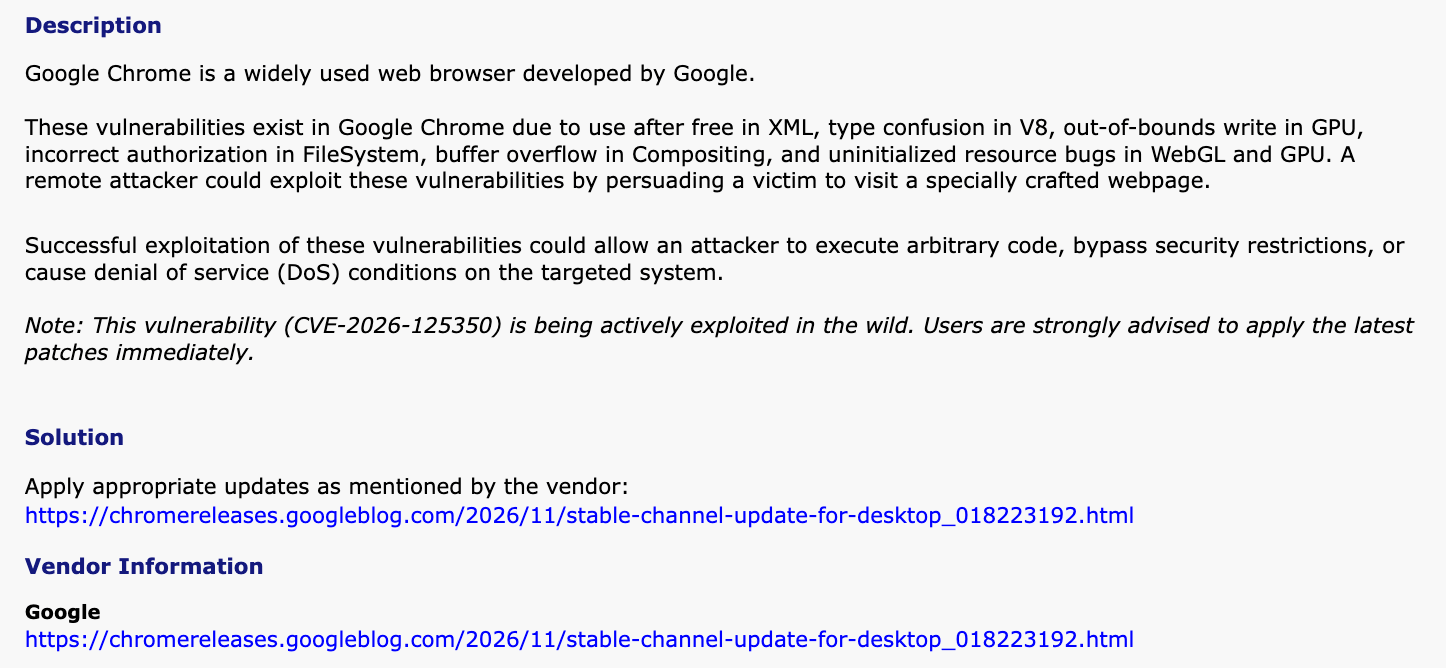
Desktop Chrome builds older than 157.0.8103.50 are affected. So are Extended Stable builds older than 156.0.8078.96. Reports mention how one flaw is already being exploited, which two of them identify as CVE-2026-125350.
| Component | Flaw type | What it means in plain English |
| XML handling | Use-after-free | Memory gets reused after Chrome has already released it; CVE-2026-125350 is of this type |
| V8, the JavaScript engine | Type confusion | Code mistakes one kind of data for another |
| GPU | Out-of-bounds write | Data lands past the edge of its assigned space |
| FileSystem | Incorrect authorization | A permission check can be sidestepped |
| Compositing | Buffer overflow | Too much data spills into neighboring memory |
| WebGL and GPU | Uninitialized resource | Memory gets used before it’s properly set up |
Also Read: The iQOO 16s Just Hit BIS And It Might Be the Only Flagship You Can Still Afford
What Could an Attacker Do?
CERT-In says a successful exploit could let bad actors run code on your computer, easily slip past Chrome’s security limits, and even crash the system. The catch, and the silver lining, is that victims need to visit a specially designed webpage for the exploitation to take place.
Even so, I’d still treat this as a genuine warning. One report I read says Google shipped a patch for the issue on November 9, 2026. That is why CERT-In advises Indian users to update their Google Chrome browsers immediately. You should ideally target version 157.0.8103.50 or newer.
Also Read: Samsung’s Galaxy S27+ Just Cleared its India Paperwork. Now About That Price
If Chrome offers you a higher number, take it.
| Where you use Chrome | How to update | What to check |
| Windows, Mac or Linux | Three-dot menu, then Help, then About Google Chrome; relaunch afterward | 157.0.8103.50 or newer (my reading); Google’s latest is .78/.79 |
| Work-managed Extended Stable | Usually your IT team’s job | Builds older than 156.0.8078.96 are affected; fixed build not stated |
| Android or iOS | Your phone’s app store | Not named as affected; one report still advises updating |
Also Read: vivo X500 Ultra launch tipped for March to April 2027 with Snapdragon 8 Elite Extreme Gen 6

You can follow Smartprix on Twitter, Facebook, Instagram, and Google News. Visit smartprix.com for the latest tech and auto news, reviews, and guides.